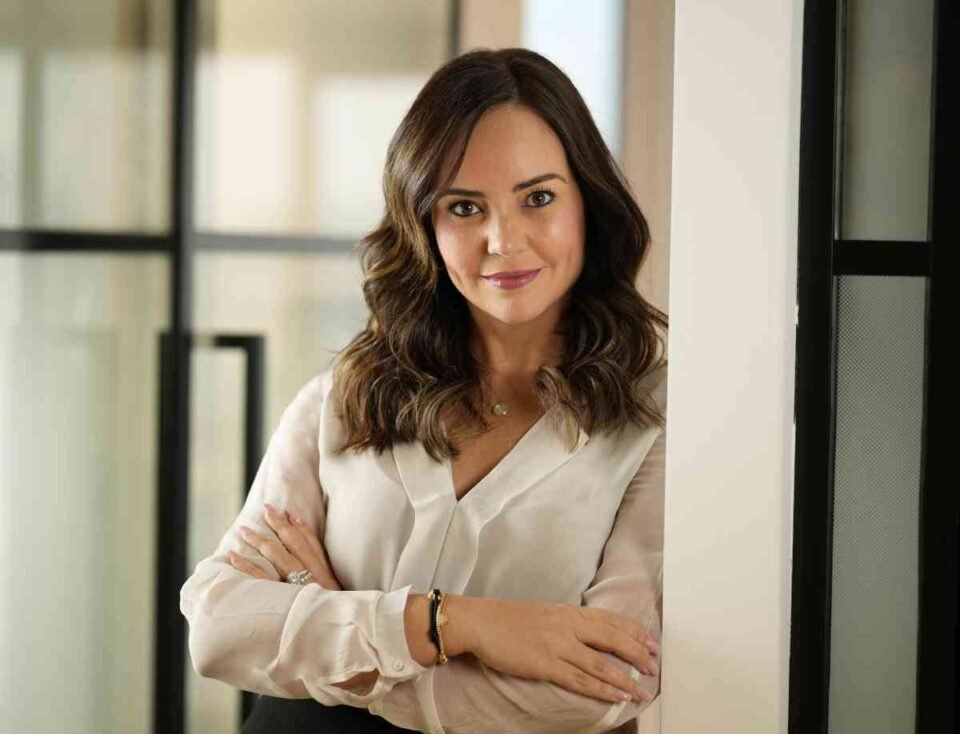
In an exclusive Q&A with Techitup Middle East at GISEC 2026, Meriam ElOuazzani, Vice President – Middle East, Turkey and Africa (META) at Censys, discusses regional expansion, attack surface visibility, and moving from reactive defense to proactive threat hunting.
Techitup Middle East: Censys made its regional debut at GISEC 2026. What were your key highlights and announcements at the show?
Meriam ElOuazzani: GISEC was our first appearance at the show under the Censys name, and I wanted us to lead with a question: what does your organization actually have facing the internet right now? Knowing what’s exposed, what’s changed, and where the risk actually sits is the starting point. Everything else depends on having that picture.
We demonstrated our Attack Surface Management and Adversary Investigations capabilities, highlighted Operation Digital Shield with Rilian in the UAE, and our partnership with Tanium. But the most useful part of the show was the pattern in the questions. Government and banking teams kept coming back to speed: once you know an asset is exposed, how quickly can you act before someone else finds it?
That was the real signal I took from GISEC. Security leaders wanted to talk about visibility and response speed, tied to the exposure problems they’re already dealing with.
Techitup Middle East: Middle Eastern enterprises are expanding rapidly across multi-cloud and hybrid infrastructure. How does Censys map unknown internet-facing assets and shadow IT across ports before attackers find them?
Meriam ElOuazzani: Most of what we find isn’t hidden by attackers. It’s hidden by an organization’s own sprawl. A team spins up a cloud instance for a pilot, another team duplicates the service in a second provider six months later, and the first system never makes it into the CMDB or never gets retired.
From the outside, both are still there. Censys continuously scans the public internet, including all 65,535 IPv4 ports, and uses automatic protocol detection to identify what is actually running. We can then connect those observations back to an organization’s attack surface: services, software, certificates, domains and cloud context. That’s how an exposed admin interface, an outdated service or a forgotten test system surfaces even when nobody put it on an inventory list.
The UAE’s 2025 cybersecurity report found that half of critical vulnerabilities remained unaddressed for more than five years. The practical lesson is that long-lived exposure deserves as much attention as the newest zero-day. As companies spread across more cloud providers, the number of places where forgotten assets can persist only grows.
Techitup Middle East: How are you helping security teams pivot from reactive incident response to proactive adversary tracking and threat hunting?
Meriam ElOuazzani: I’d push back slightly on the word “pivot.” Most teams I meet aren’t choosing between incident response and threat hunting. They’re consumed by the first and never build capacity for the second. One cybersecurity organization’s 2026 data puts mean time to exploit at an estimated minus seven days, meaning exploitation can begin before a patch exists. Another puts average eCrime breakout time at 29 minutes. Those are different clocks, but they point to the same operational reality: defenders have very little time once an exposed weakness becomes actionable.
What we give teams is an outside-in view of both their own internet-facing footprint and adversary infrastructure: exposed remote-access services, forgotten VPNs, certificates, domains and the infrastructure around suspicious activity. In practice, proactive hunting starts with knowing what exists, what changed and what is newly reachable. That gives analysts a place to look before the first internal alert fires.
I want threat hunters and incident responders working from the same current picture of the internet.
Techitup Middle East: How is Censys helping operators secure exposed ICS/SCADA assets without disrupting operational continuity?
Meriam ElOuazzani: ICS and SCADA environments carry a constraint most enterprise networks don’t: you may not be able to patch or reboot a controller without affecting a production line, utility process or other physical operation.
Systems that should not be directly reachable from the public internet can become targets of opportunity.
Censys helps operators identify that exposure from the outside.
We don’t deploy agents on control equipment, and we don’t require authenticated access. Our scanners use protocol-level handshakes to identify externally reachable services. That can surface exposed HMIs, PLCs, remote-access interfaces and other control surfaces so the operator can decide how to isolate, firewall or otherwise remediate them within existing maintenance and change-control processes.
That distinction matters in OT. Censys requires no agent or installed software to identify externally observable exposures, allowing operators to assess risk without adding another component to the operational environment.
Techitup Middle East: Continuous Threat Exposure Management (CTEM) is a high priority for regional CISOs. How does Censys integrate with existing SIEM, SOAR, and risk workflows to ensure rapid, actionable remediation?
Meriam ElOuazzani: CTEM only earns its keep if exposure data changes what the team does next. We integrate with the systems security teams already use, SIEM, SOAR, ITSM, CMDB, and vulnerability workflows, so a newly exposed service, a new high-risk finding or a change in the attack surface can enter existing investigation and remediation processes directly.
Prioritisation is the harder part. An information security research company’s latest research on the Gulf found vulnerability exploitation was the most common initial-access vector, accounting for 38% of attacks. Severity becomes much more useful when a team can also see whether the vulnerable software is internet-reachable, whether the vulnerability is known to be exploited, how recently the exposure appeared and who owns the asset.
Censys provides that external context, and integrations with platforms such as Splunk, ServiceNow and Jira let teams operationalise it in the workflows they already trust. For me, that’s the test of CTEM: how quickly can the organisation move from seeing an exposure to putting it in front of someone who can fix it?
